Mobile Security Workspace
Everything you need to break,analyze, and secure mobile applications.
MobLizer unifies Android and iOS device management, reverse engineering, runtime instrumentation, network analysis, API testing, filesystem inspection, and AI-assisted security research into one workspace.
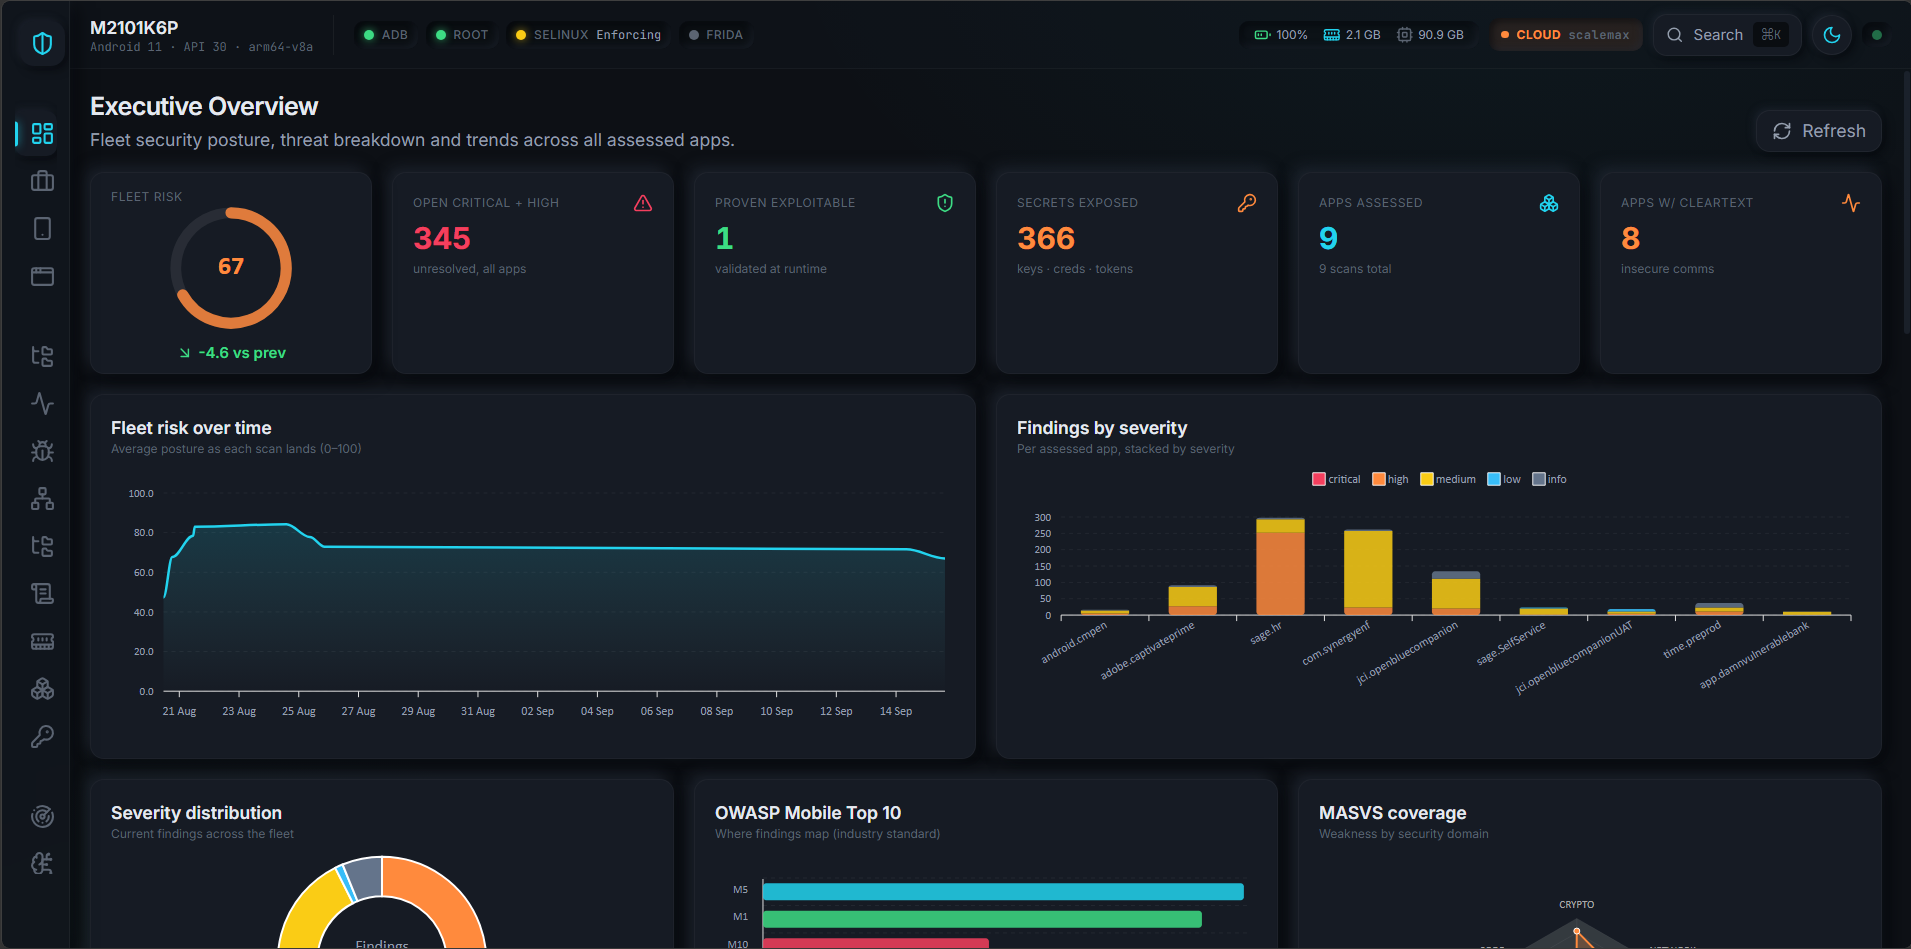
THE PROBLEM
Stop switching between tools.
Traditional mobile pentesting means constant context switching between ADB, Burp Suite, Frida, JADX, MobSF, Objection, terminals, and more.
One connected investigation.
One Workspace
Everything stays inside the same assessment context.
Runtime + Static
Move directly from source analysis to runtime behavior.
Device-Aware
Your Android/iOS device becomes part of the workspace.
AI-Powered
Analyze code, traffic, runtime output, and vulnerabilities.
PRODUCT
One workspace. Every attack surface.
Explore MobLizer's integrated modules designed for every phase of mobile security assessment.
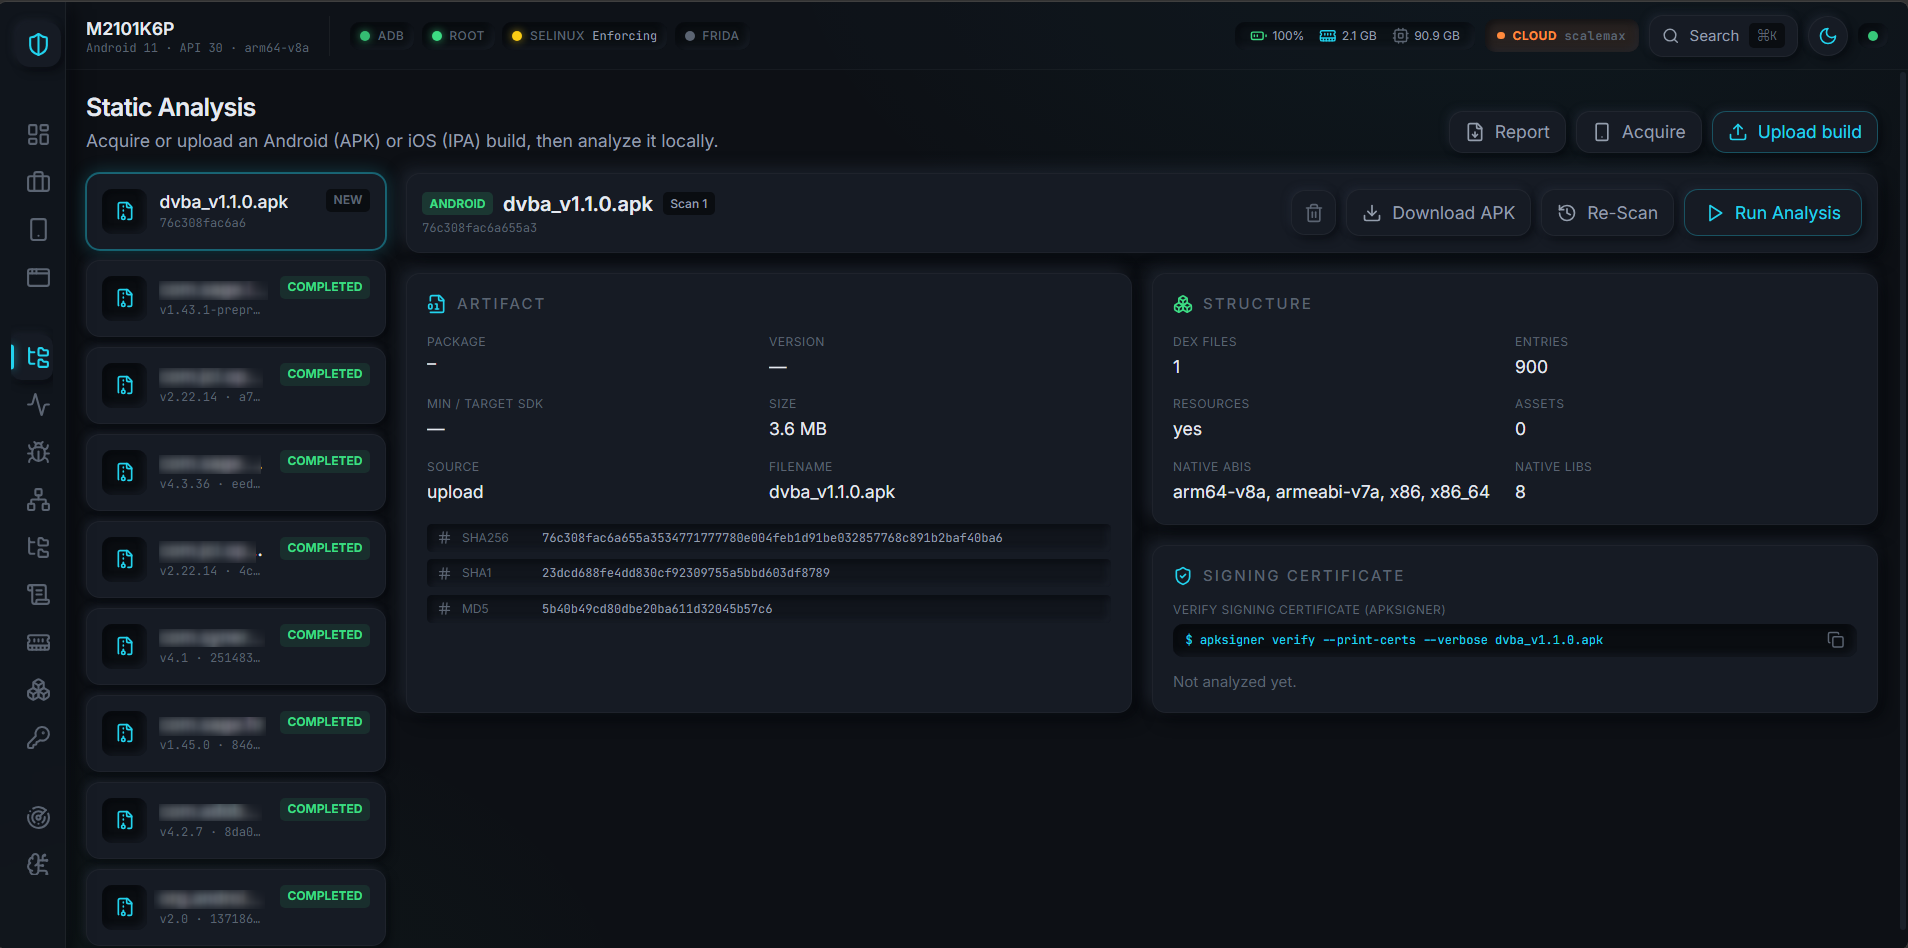
ANDROID
Go deeper than the APK.
From acquisition to source analysis, manifest inspection, and runtime testing — MobLizer covers the full Android attack surface.
iOS
Mobile security shouldn't stop at Android.
MobLizer provides comprehensive iOS application security testing with the same unified workflow.
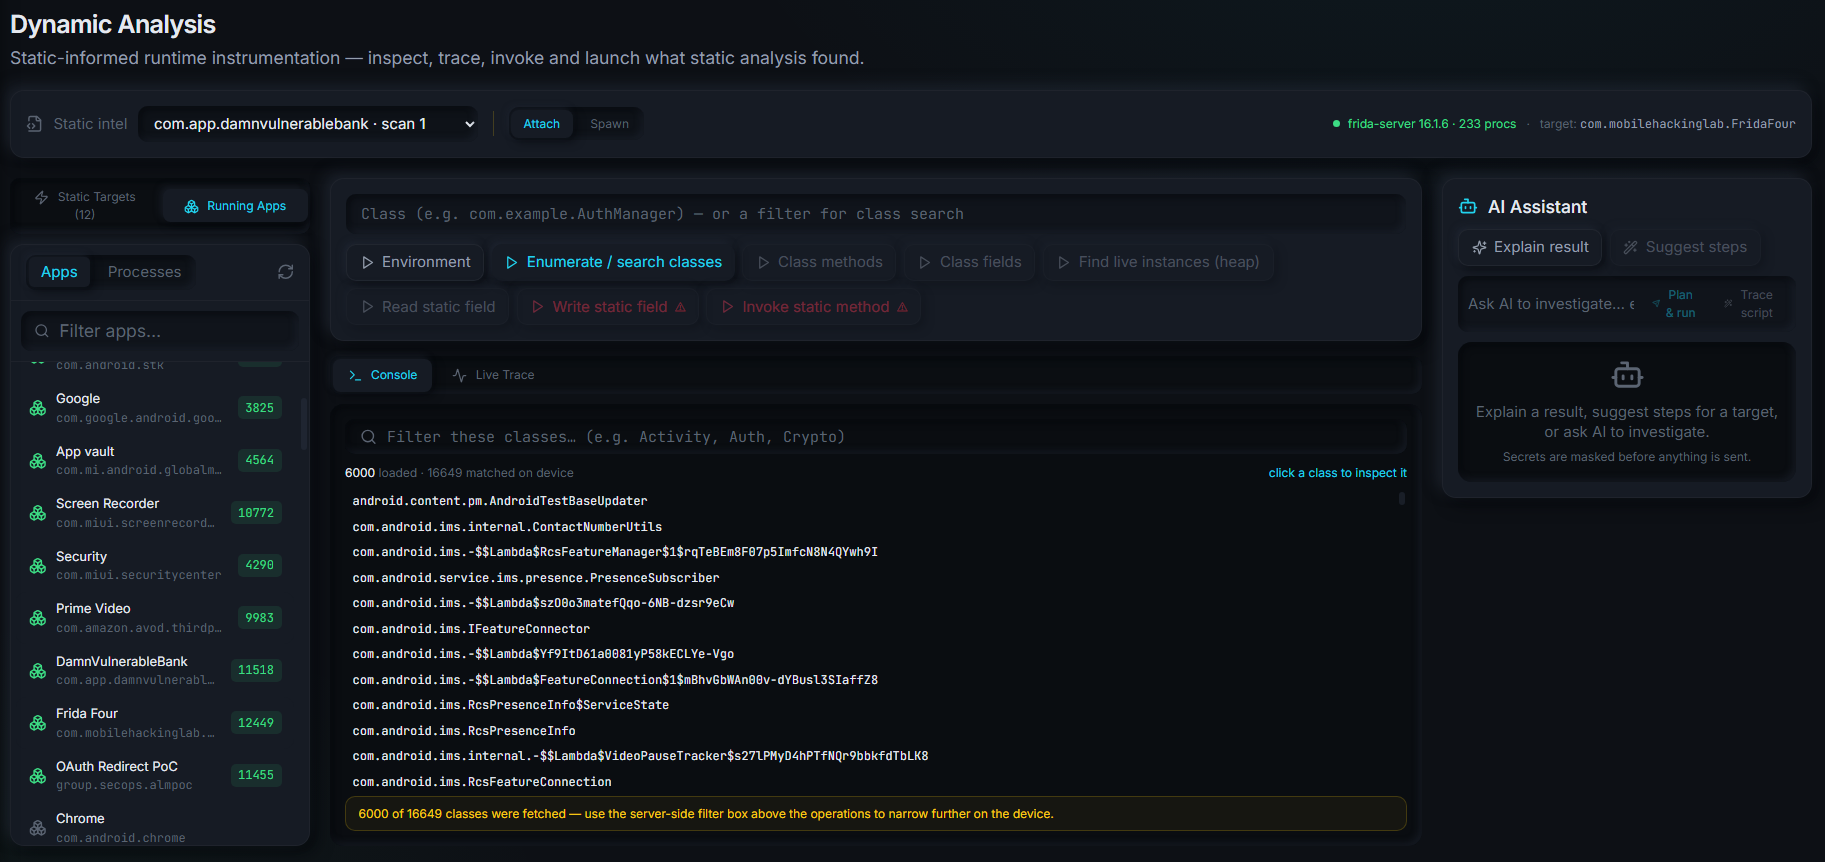
NETWORK
See what the application actually sends.
Professional HTTP/HTTPS traffic inspection with Burp Suite and mitmproxy integration.
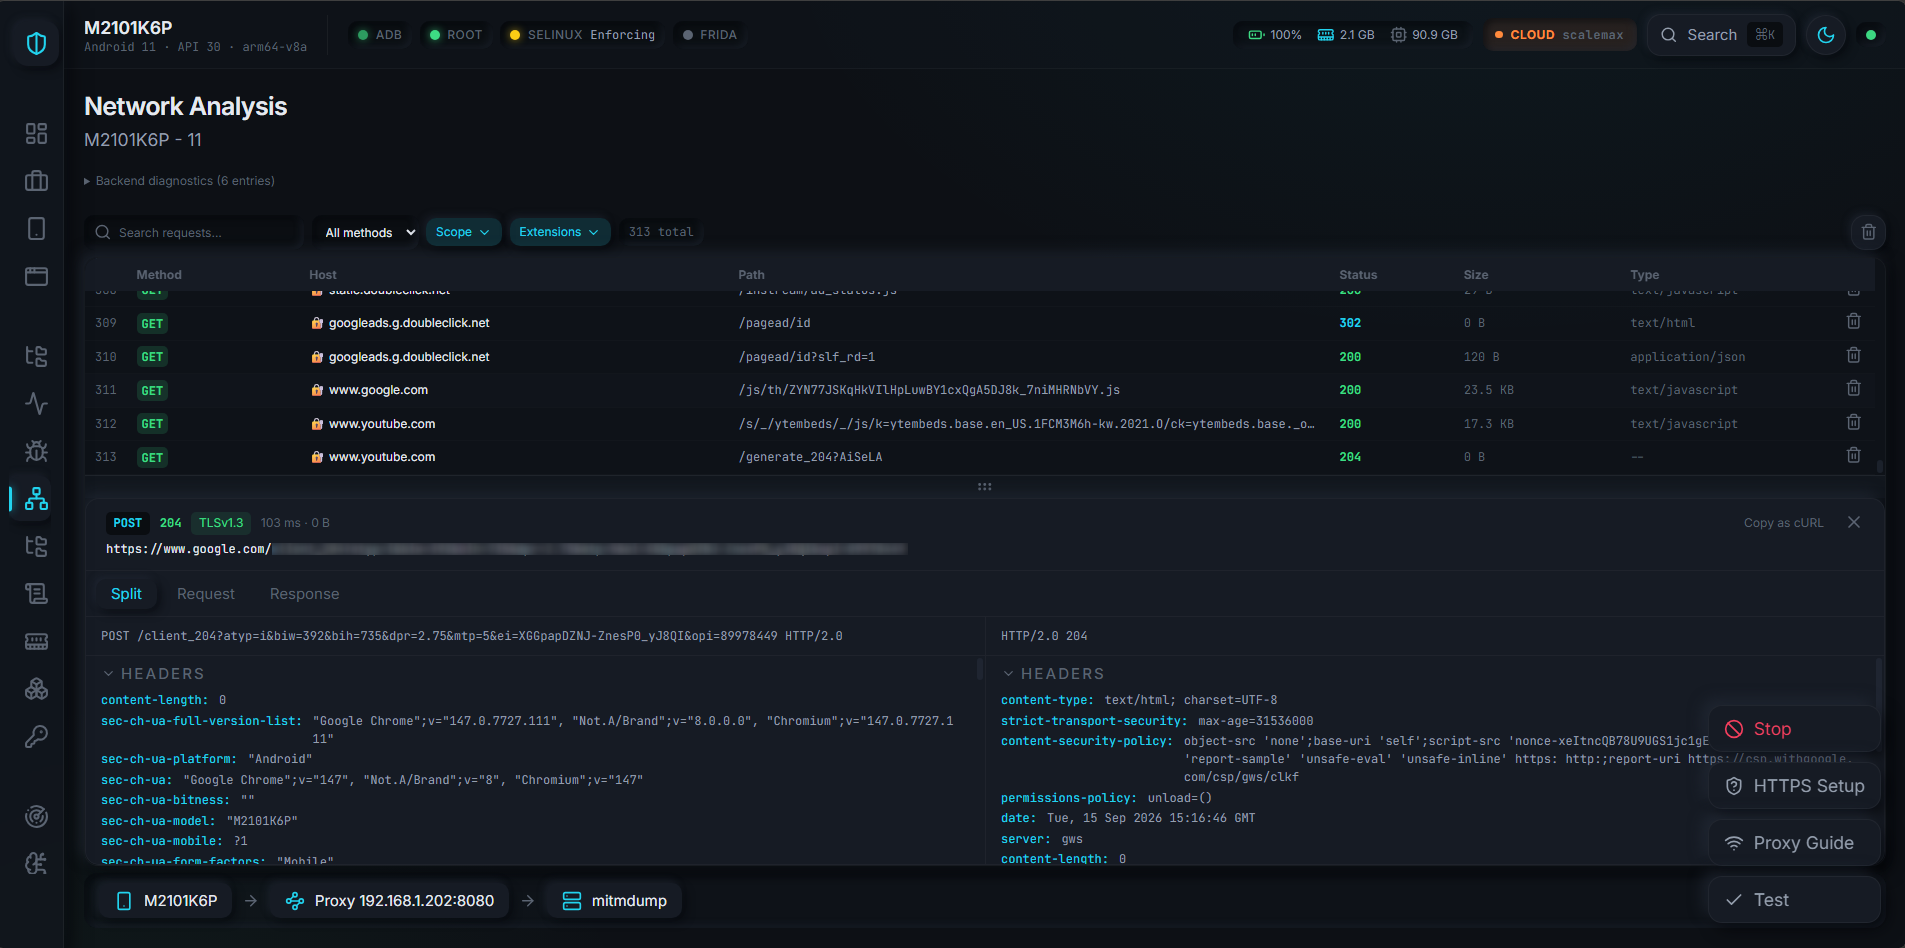
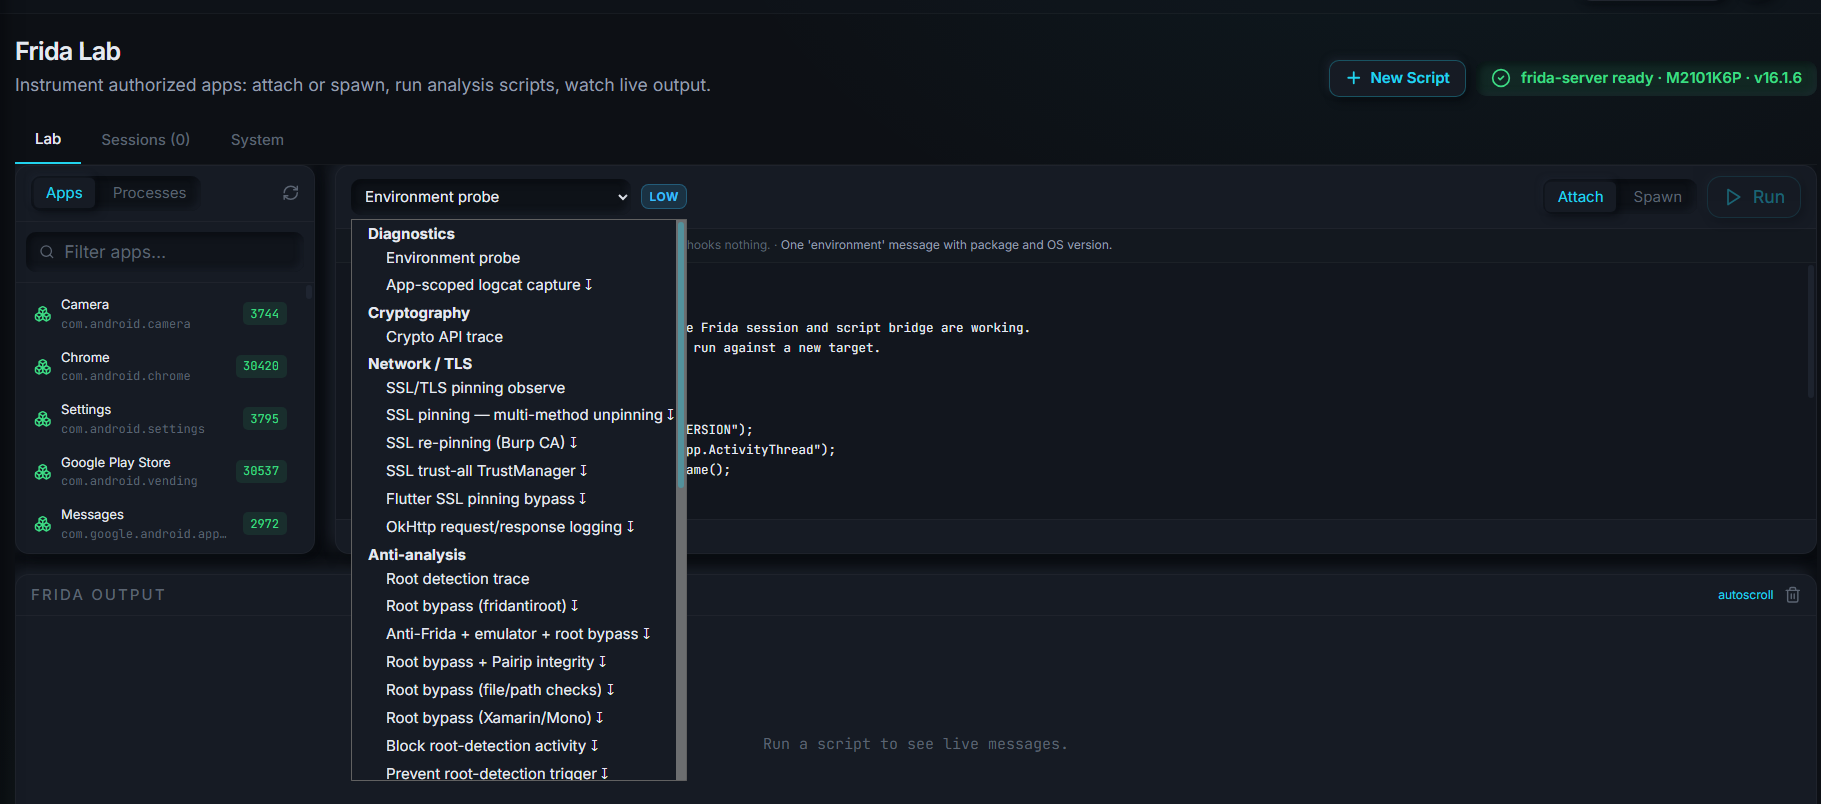
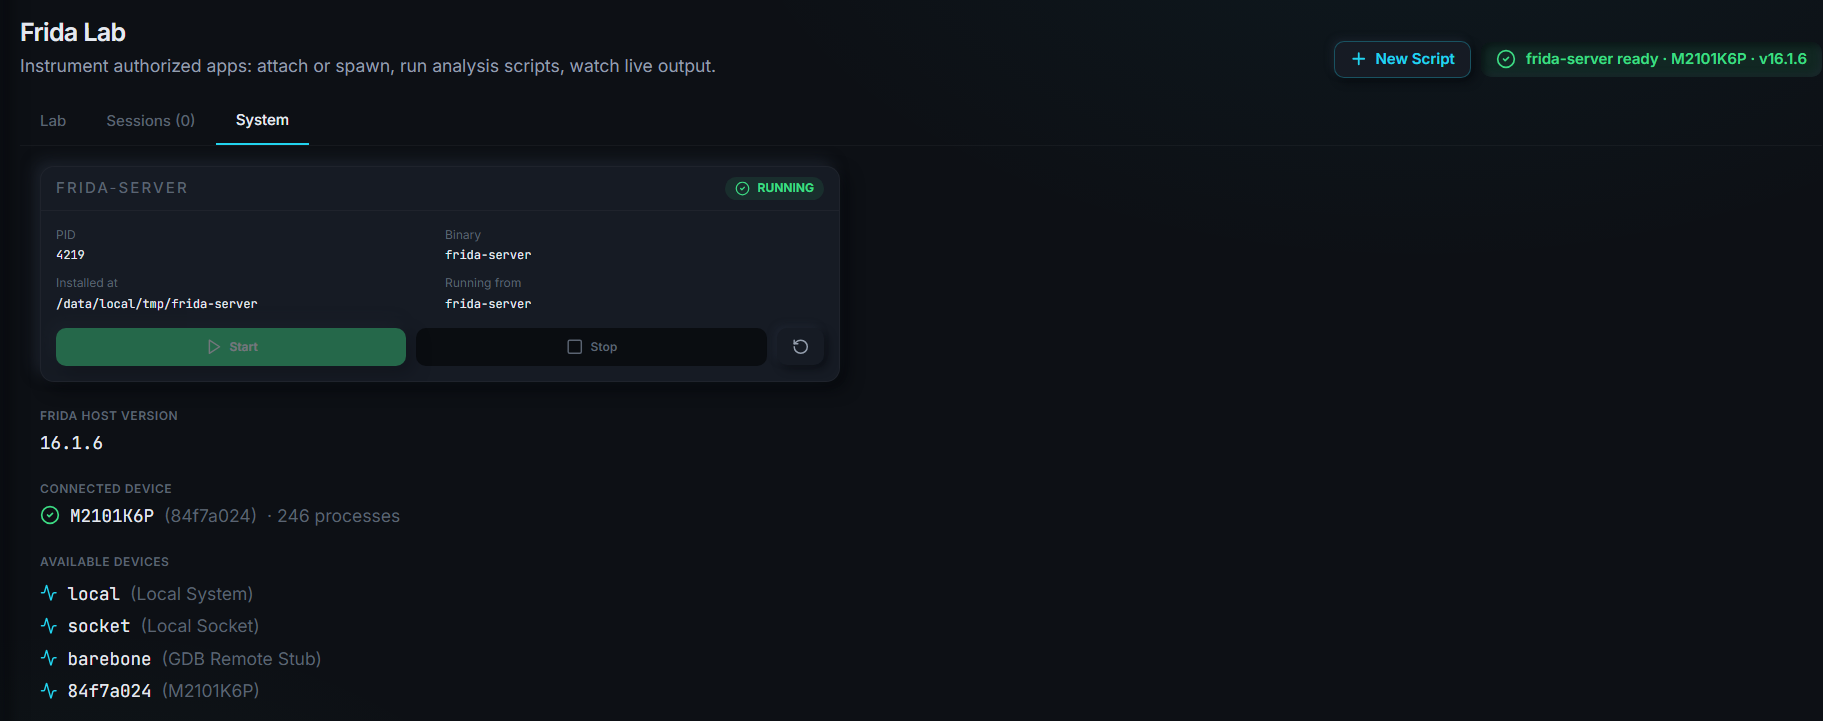
FRIDA LAB
Instrument the application while it runs.
Attach, spawn, hook, and trace with a curated script library covering SSL pinning, root detection, crypto, and more.
DEVICES
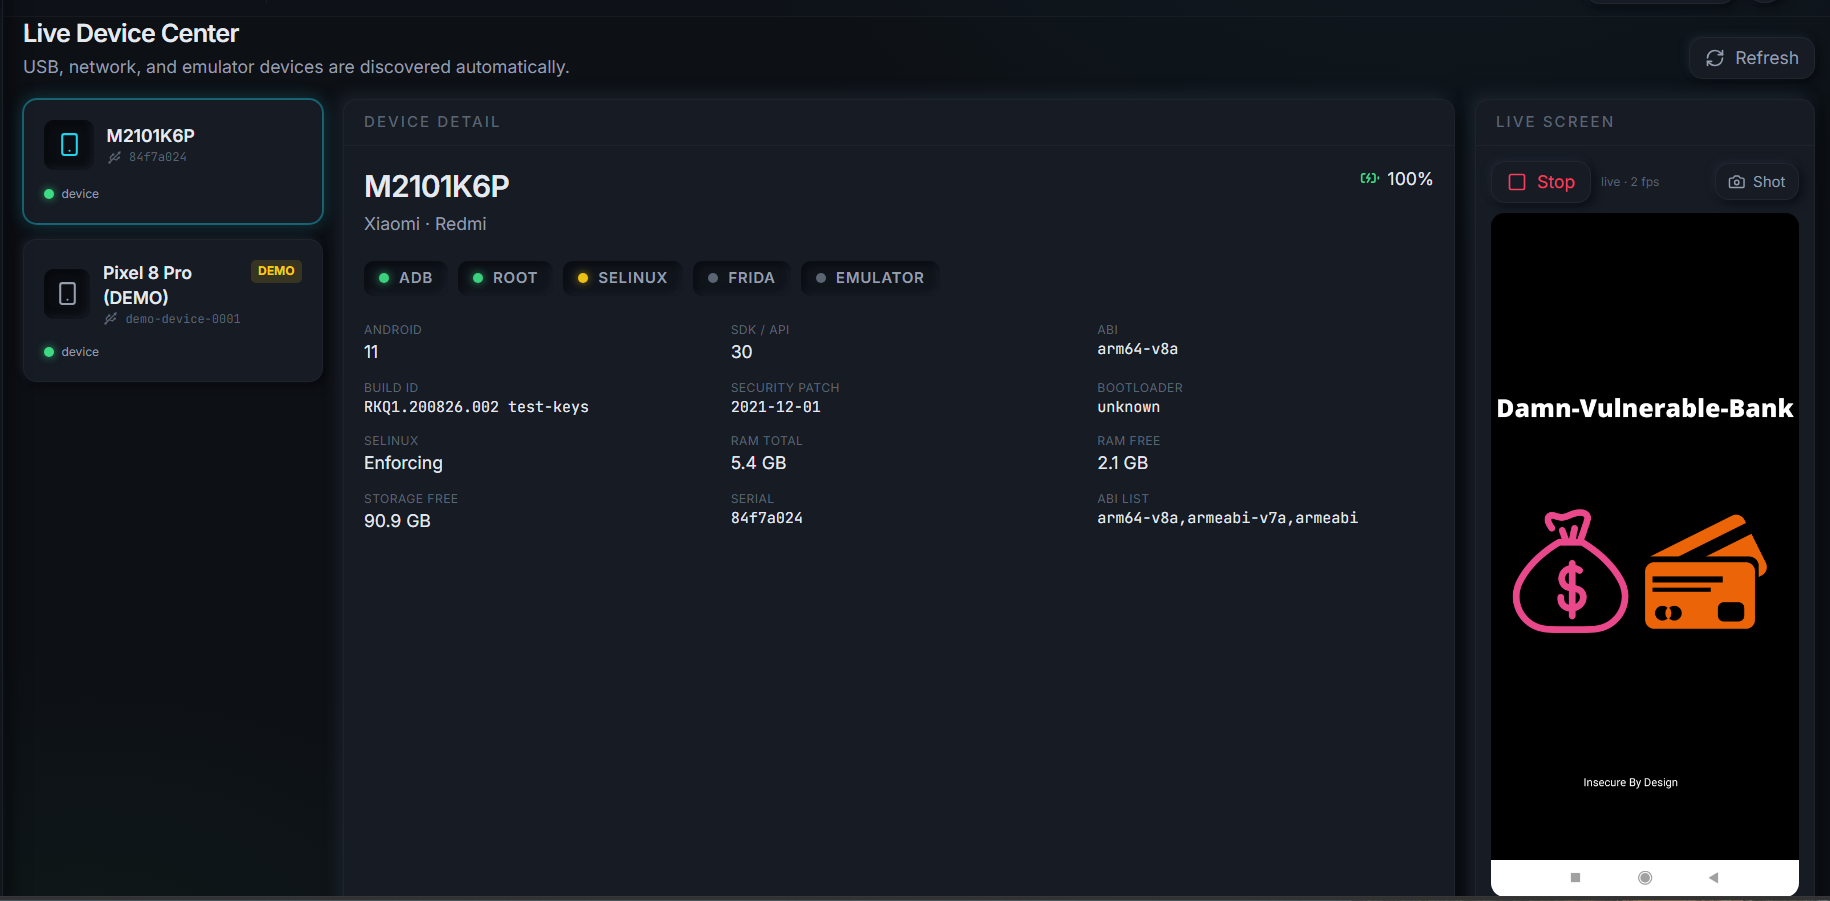
Start with the device.
Auto-discover USB, network, emulator, and Genymotion devices with full metadata and live status.
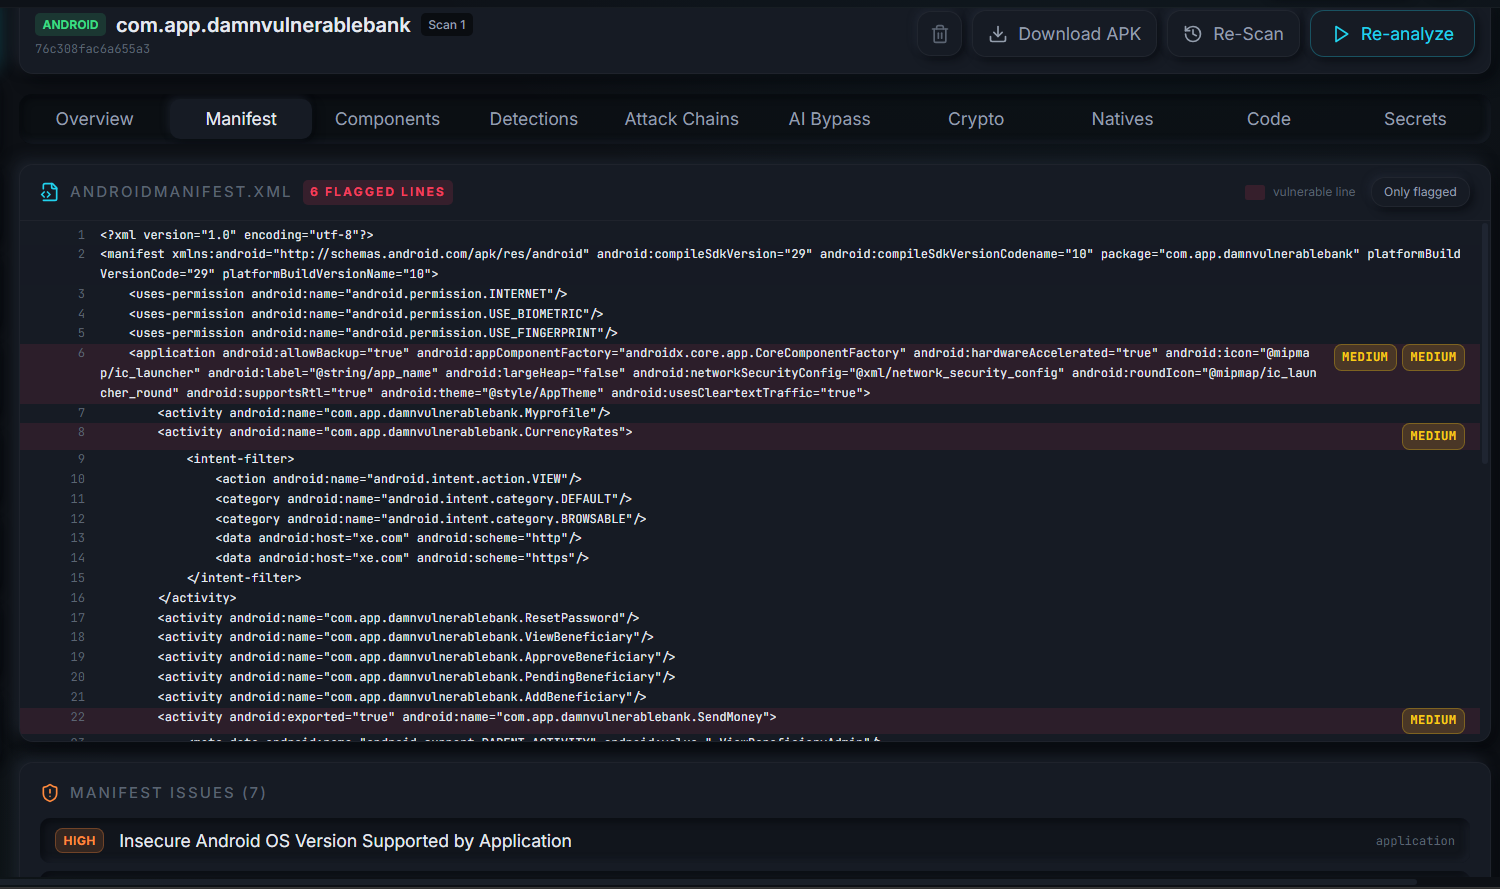
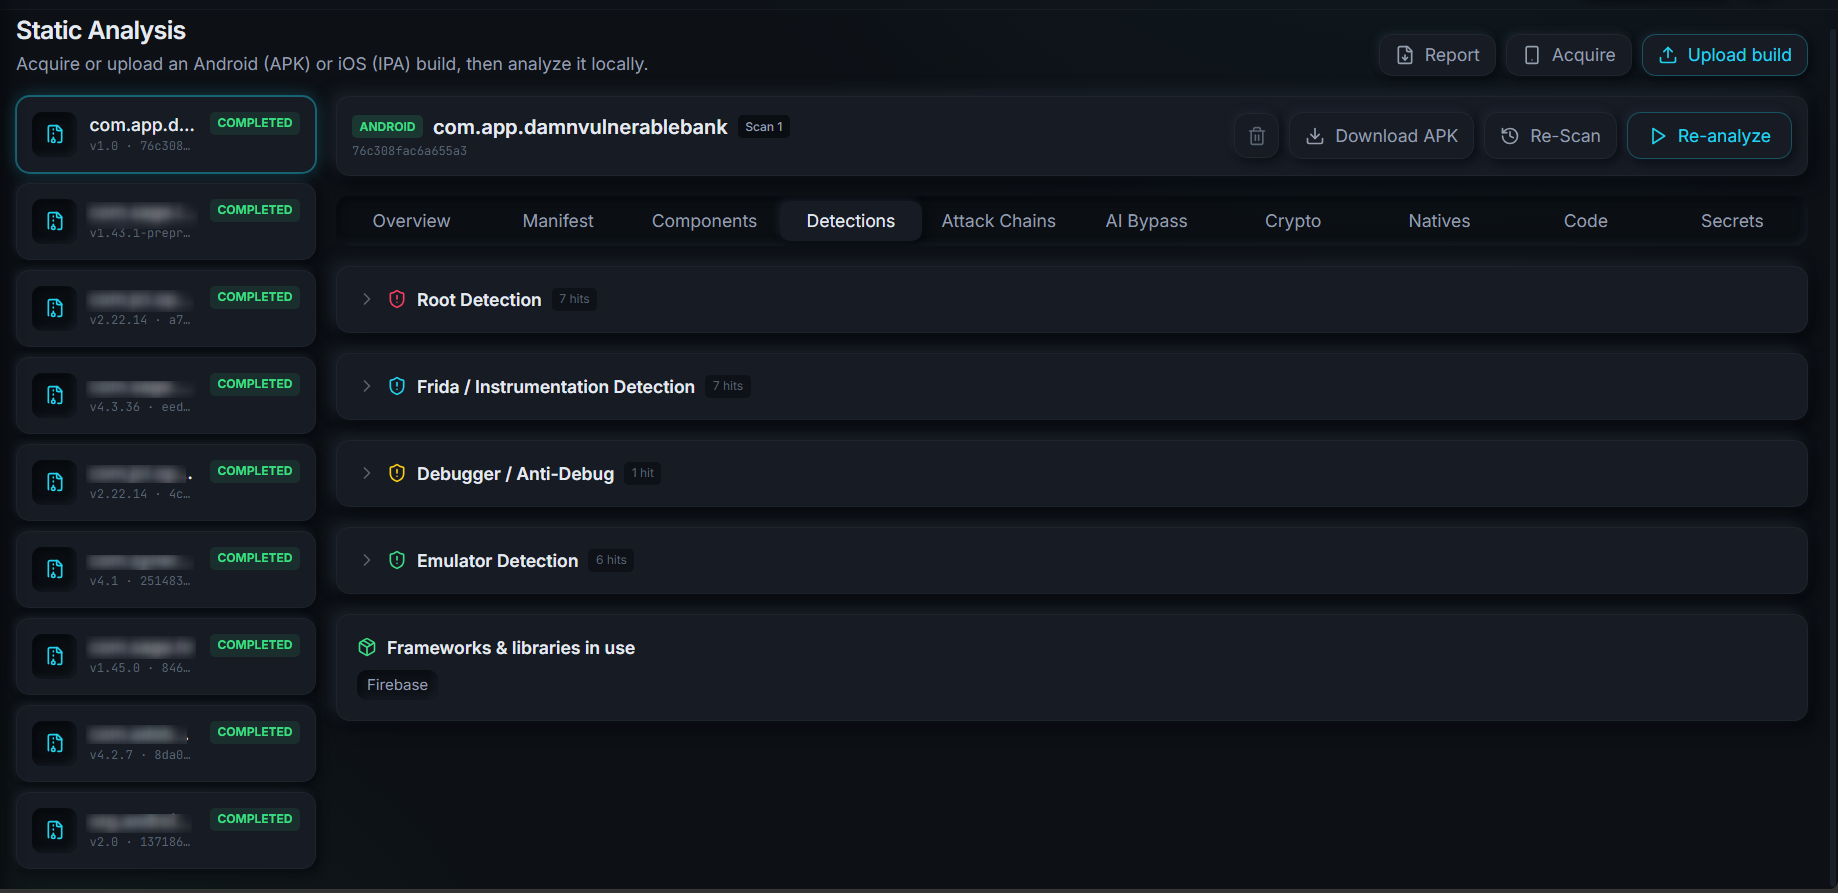
SOURCE & ANALYSIS
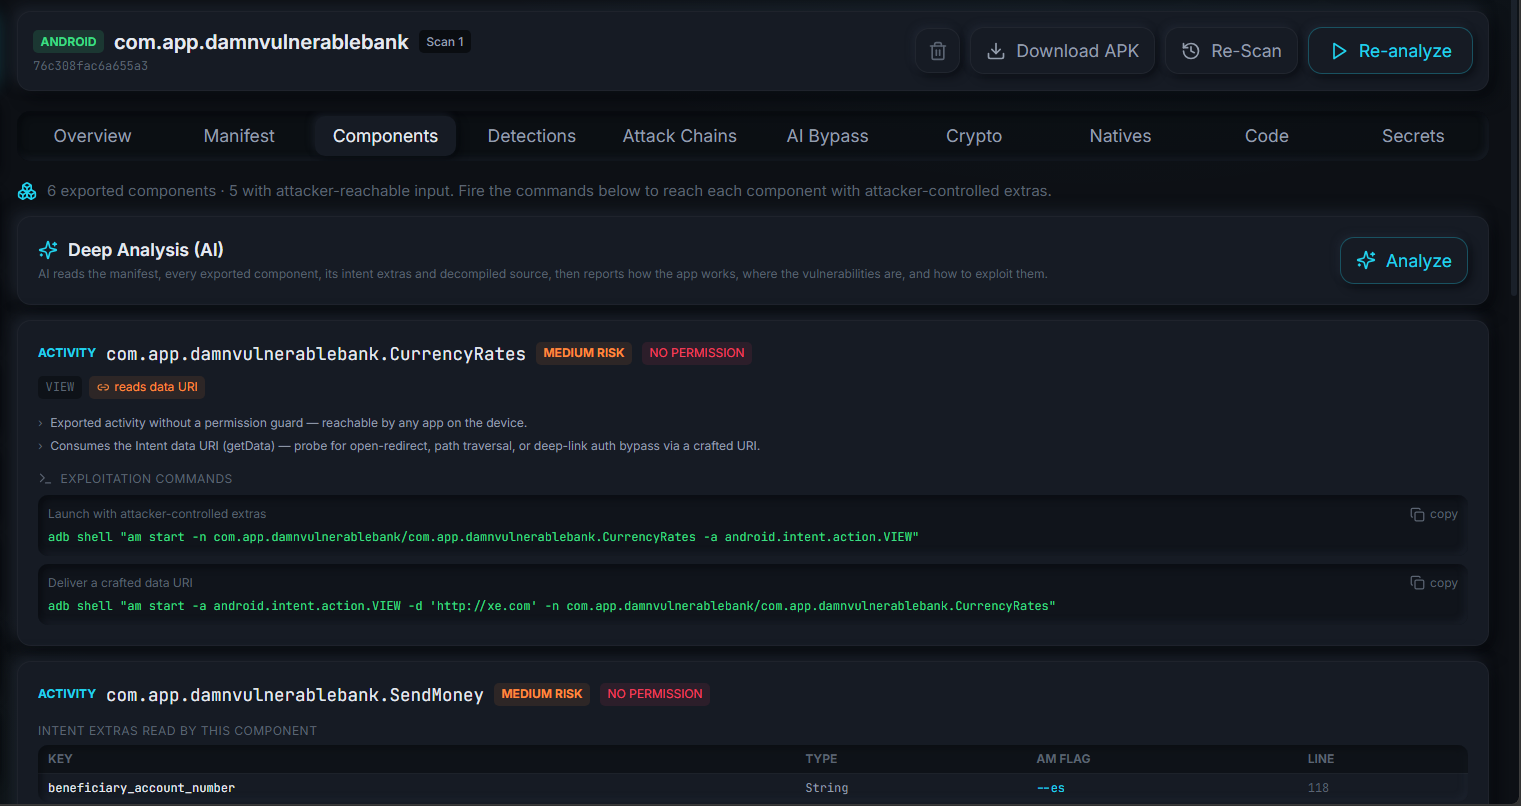
From binary to source.
JADX-style code viewer with Monaco Editor, AI analysis panel, and integrated security insights.
STORAGE & LOGS
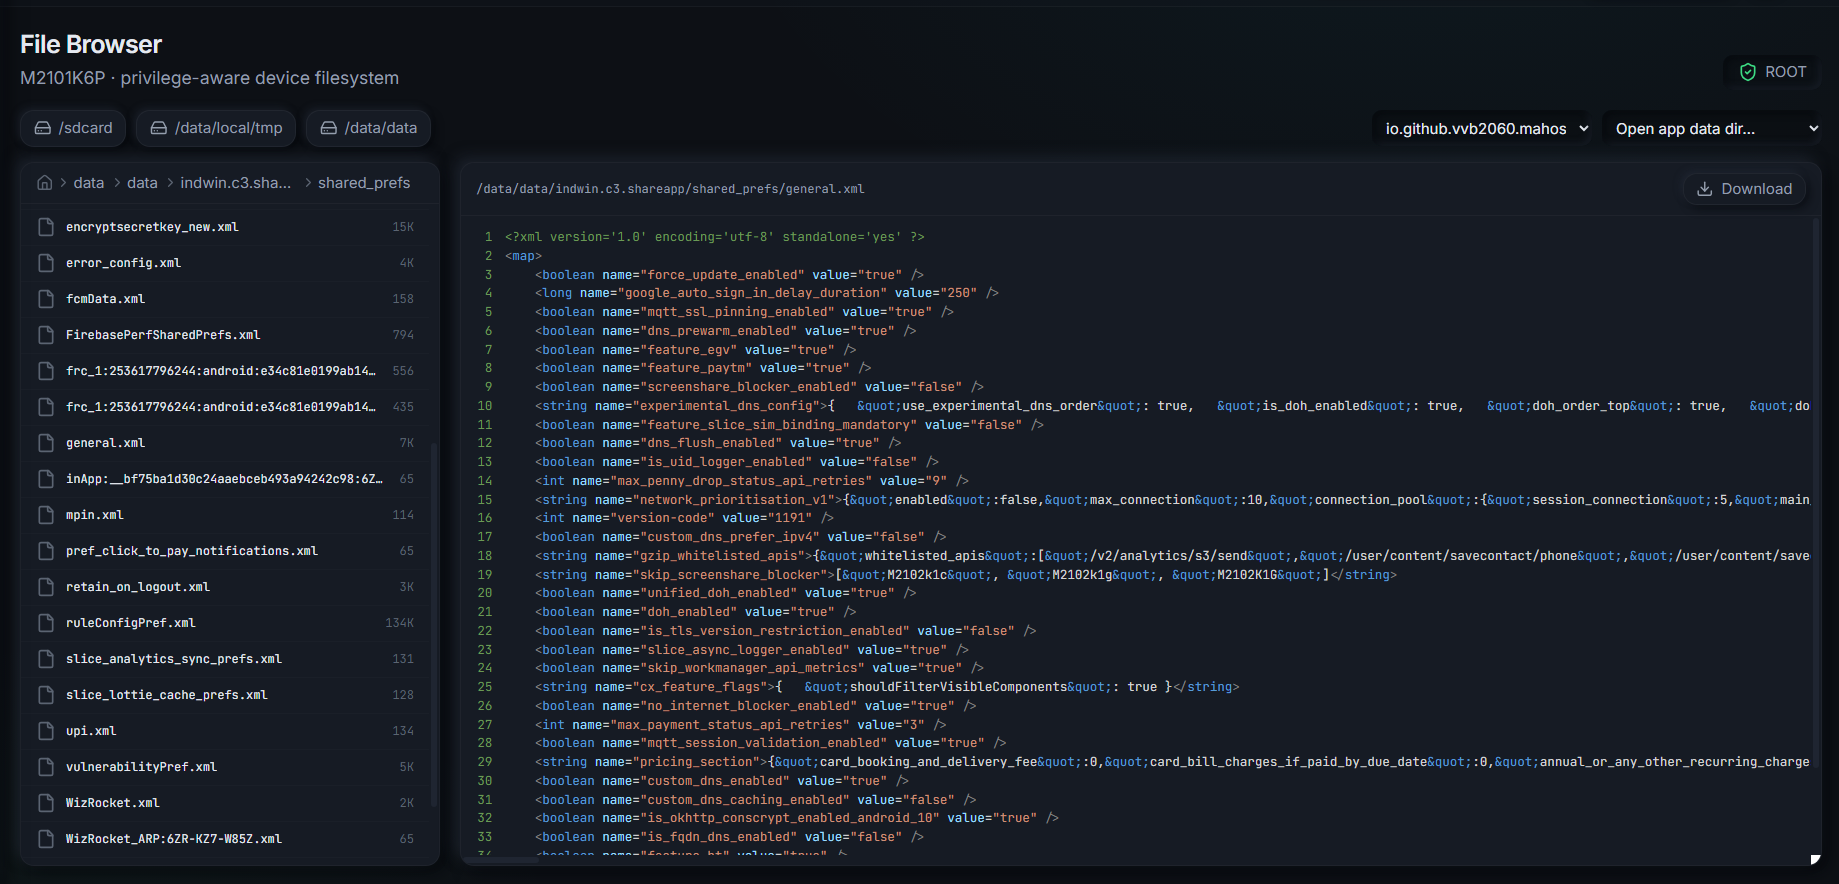
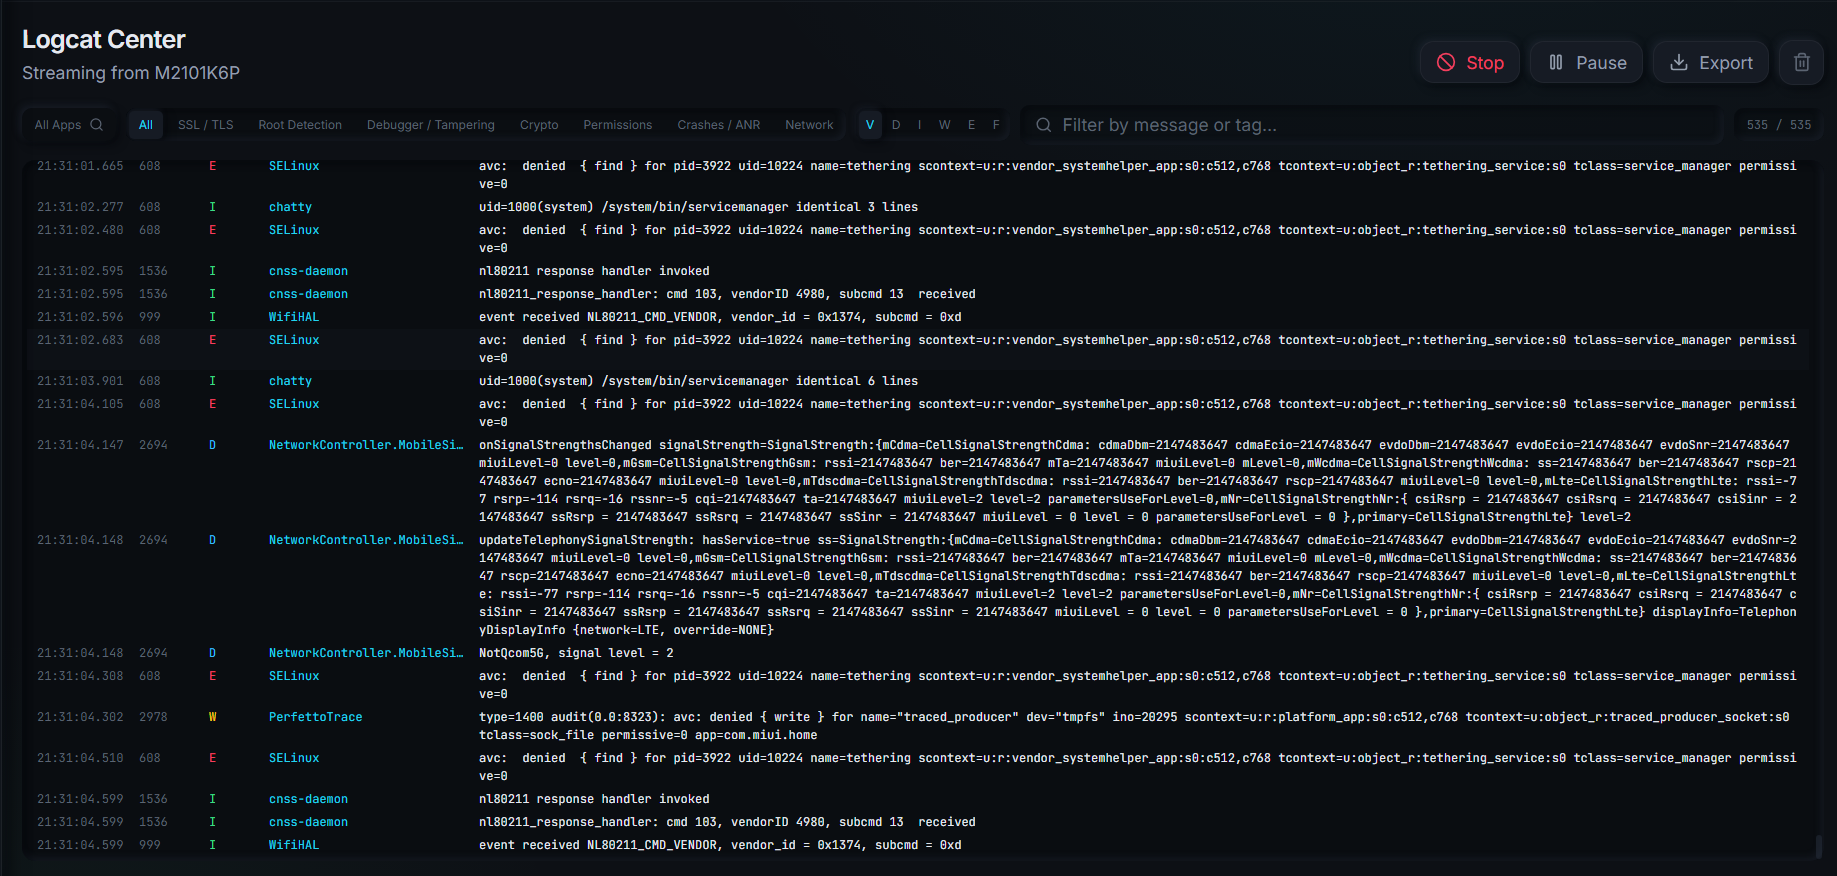
Find what the application leaves behind.
Inspect filesystem, SharedPreferences, SQLite databases, and real-time logcat streams.
AI COPILOT
Don't just collect evidence. Understand it.
AI-assisted security analysis with support for Ollama, OpenAI, and Anthropic Claude.
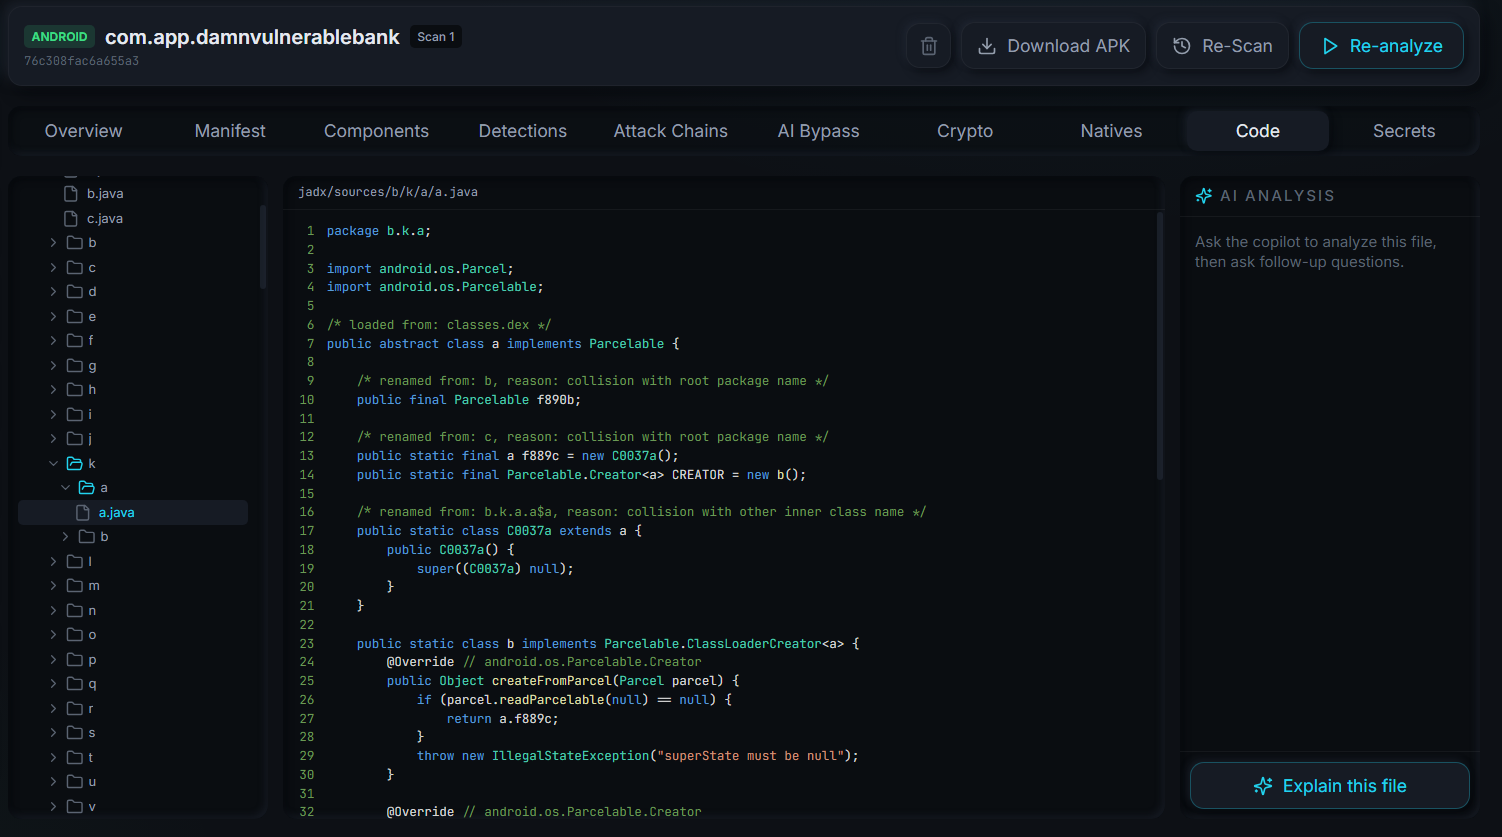
Explain Code
AI identifies security-sensitive behavior and potential vulnerabilities.
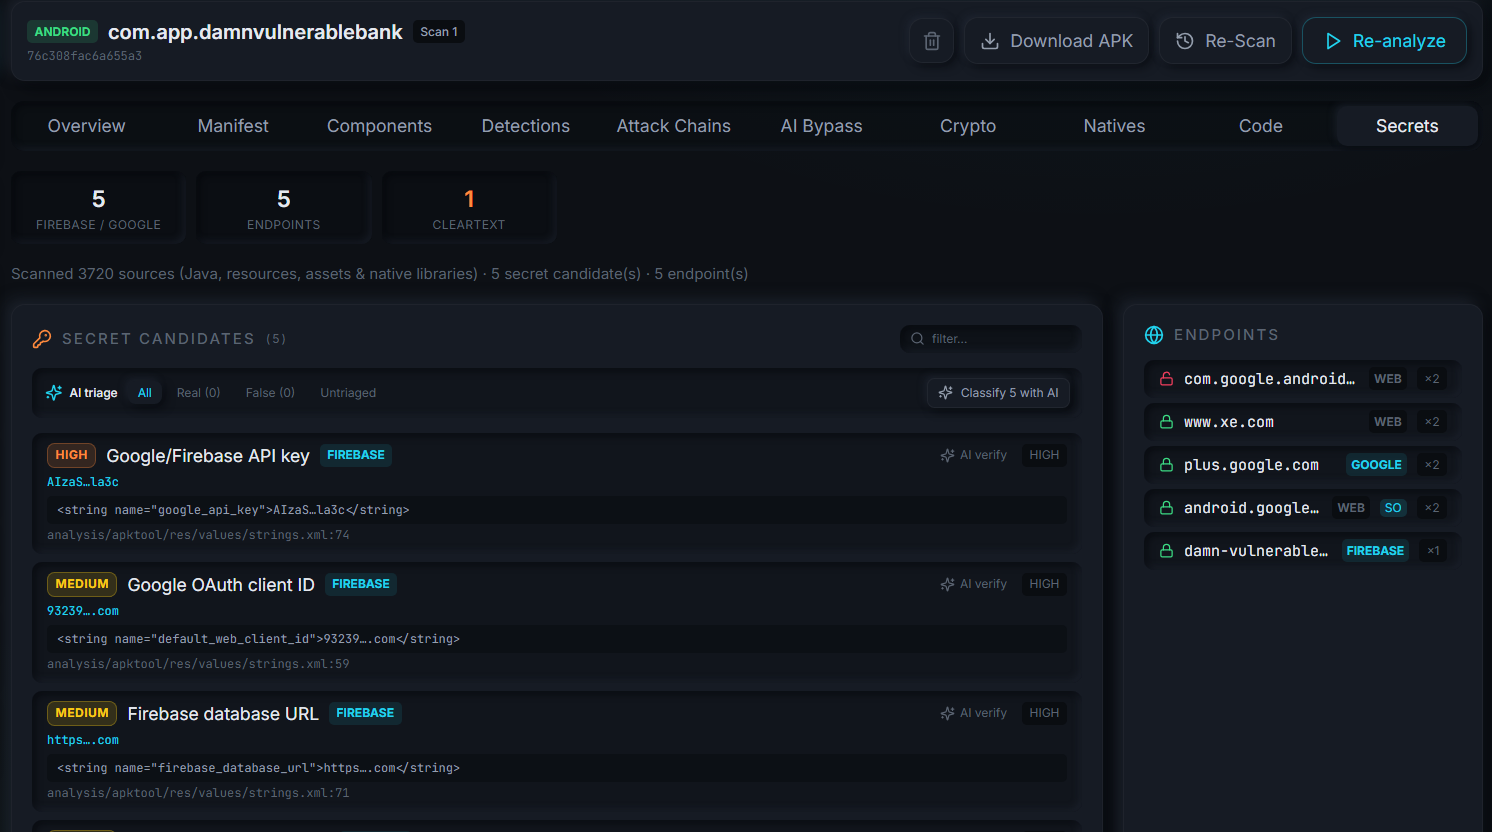
Analyze Requests
AI identifies authentication, tokens, and sensitive parameters.
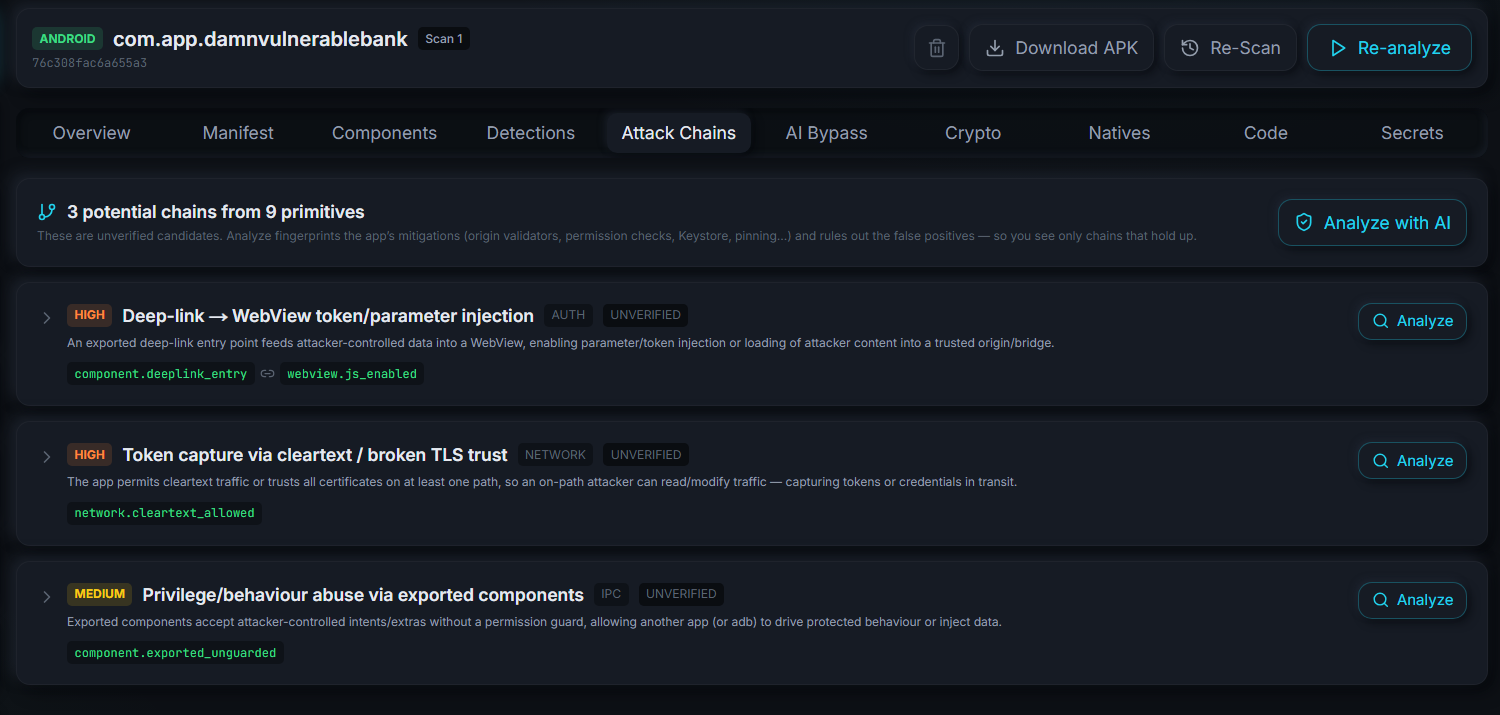
Attack Chains
AI connects findings into potential attack paths.
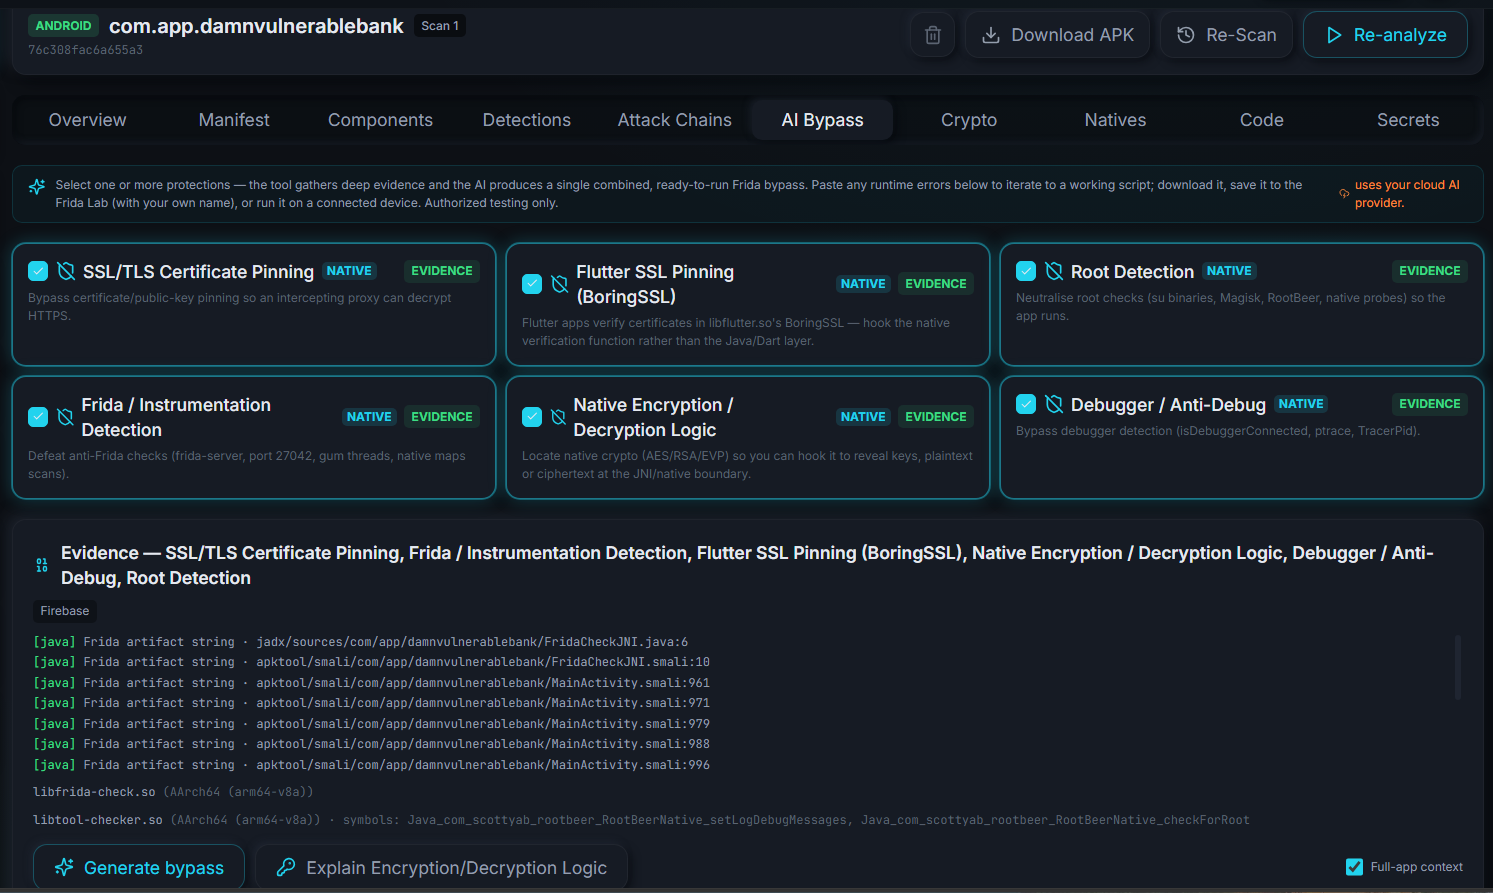
Frida Scripts
AI generates focused runtime instrumentation scripts.
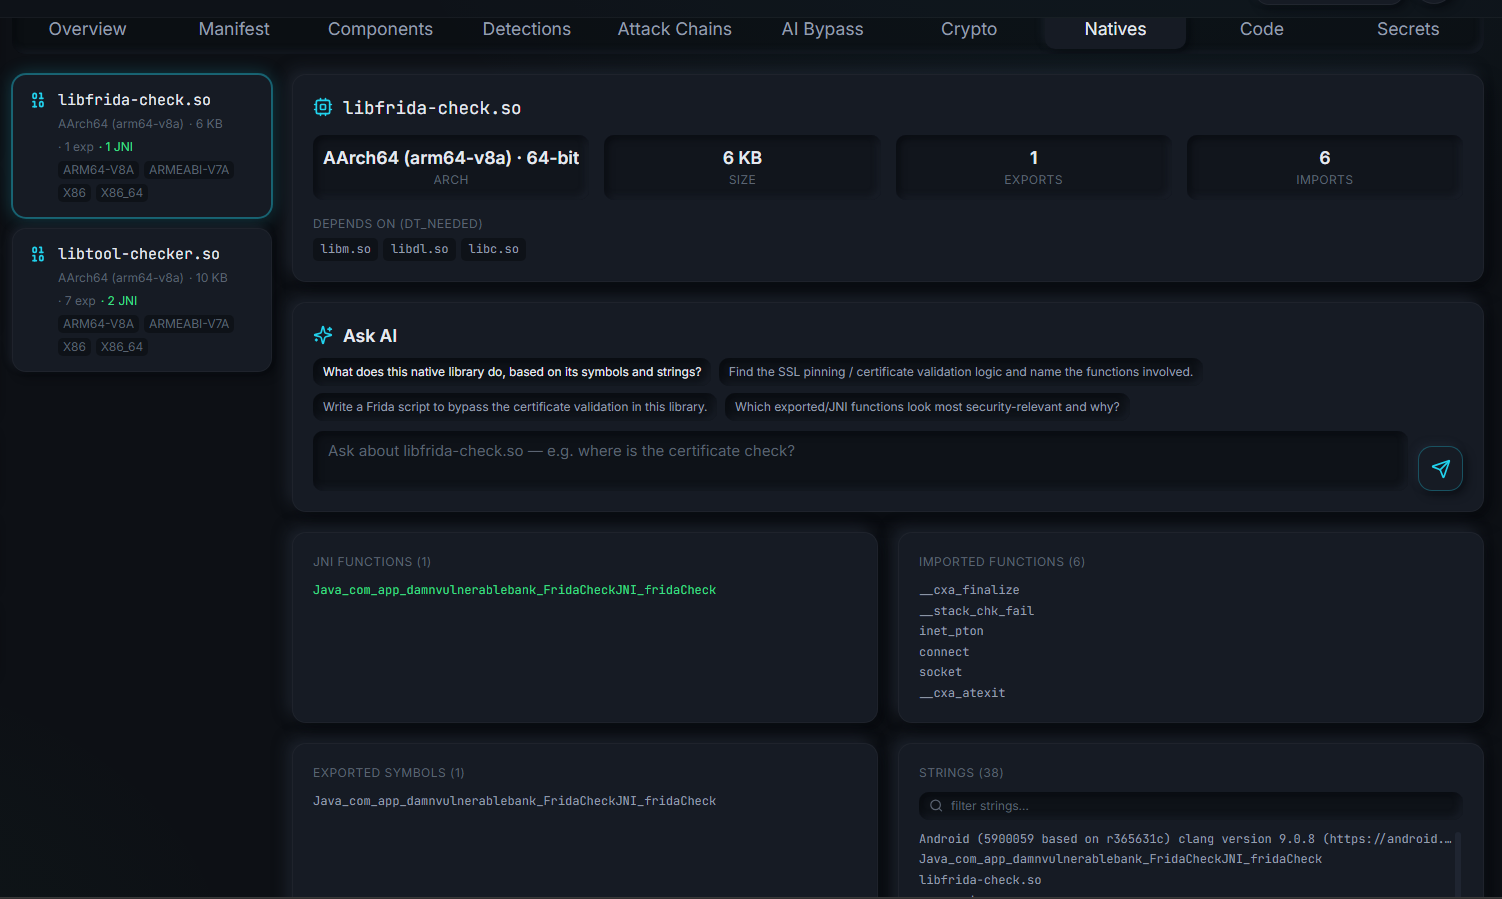
Native Analysis
AI correlates .so files with security findings.
APK Analysis
AI correlates manifest, source, and runtime behavior.
WORKFLOW
Complete mobile assessment in 8 steps.
From device connection to final report — every step in one workspace.
Connect
Connect Android / iOS device
Select
Choose target application
Discover
Map attack surface
Analyze
Static + source inspection
Instrument
Frida runtime testing
Intercept
Network traffic analysis
Exploit
Validate security issues
Document
Generate evidence & reports
BUILT FOR
Security engineers who demand more.
MobLizer is designed for professionals who need comprehensive mobile security testing capabilities.
Mobile Pentesters
Reduce tool switching and speed up assessments.
AppSec Engineers
Understand mobile attack surfaces faster.
Bug Bounty Hunters
Move from recon to exploitation quickly.
Security Consultants
Keep evidence and testing context together.
Security Researchers
Experiment with runtime instrumentation.
Red Teamers
Comprehensive mobile attack surface coverage.
TECHNICAL FOUNDATION
Built on proven tooling.
MobLizer orchestrates industry-standard security tools through a unified interface.
Your next mobile assessment
starts here.
Connect a device. Pick an application. Start investigating.